September 23, 2026
Expert checklist for Cybersecurity Month: Five things to do
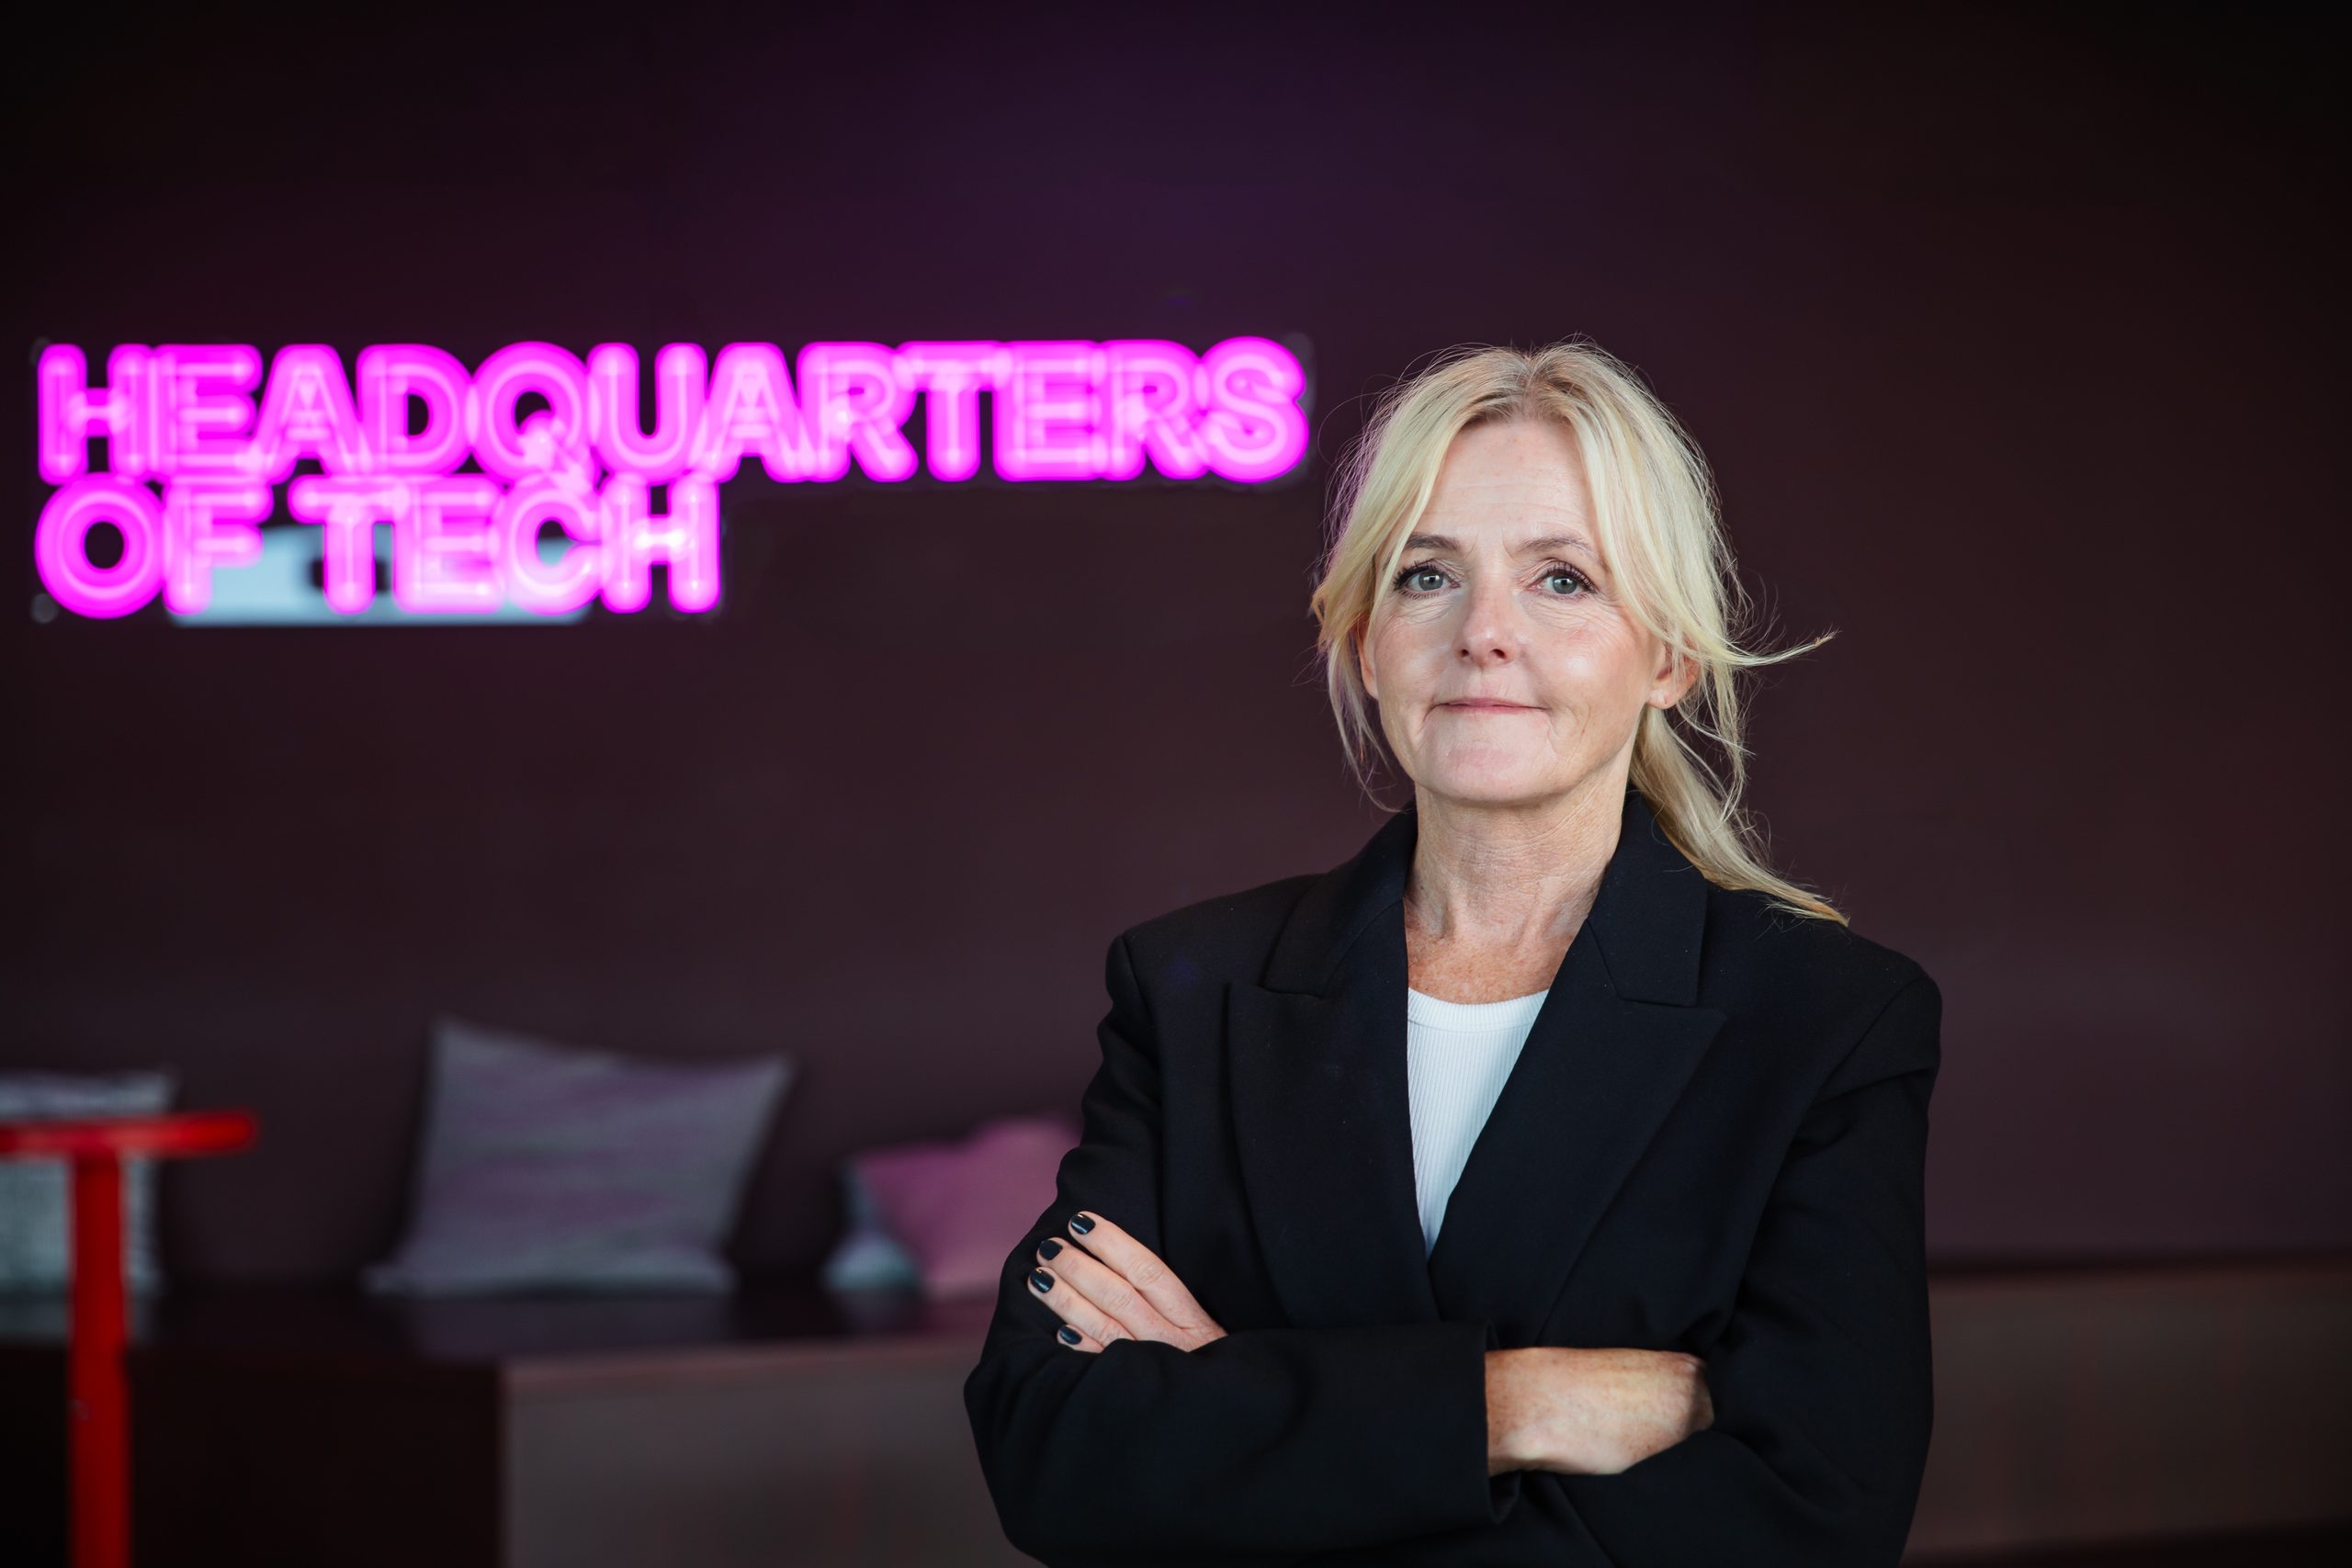
On 1 October, cybersecurity requirements will become more specific, just as European Cybersecurity Month begins. This will be the first Cybersecurity Month since the requirements of Sweden’s Cybersecurity Act were set out in more detailed regulations. HiQ cybersecurity expert Pernilla Rönn explains what is changing and which actions companies and organisations should prioritise.
European Cybersecurity Month was launched in 2012 to raise awareness of cybersecurity among citizens and organisations. The need remains significant. In August, Swedish organisations faced an average of 2,470 cyberattacks per week, an increase of 38 per cent compared with the same month last year. That is well above the global increase of 22 per cent, according to Check Point Research.
“The new regulatory framework makes cybersecurity a clearer operational and leadership responsibility. Having policies and procedures in place is no longer enough. Organisations need to be able to show that they work in practice,” says Pernilla Rönn, cybersecurity expert at HiQ.
The next phase of Sweden’s cybersecurity regulation begins on 1 October. New regulations will then take effect, specifying requirements for security measures and management training, as well as rules on security audits and security scans.
From 1 October, the following will apply:
- Specific security measures: Organisations need a structured approach to areas such as risk assessments, access controls, incident management, business continuity and supply chain security.
- Management training: Senior management needs sufficient knowledge to understand cyber risks, take responsibility for security and follow up on the organisation’s efforts.
- Security audits: A supervisory authority may require an organisation to undergo a security audit to verify that its security measures and processes work in practice.
- Security scans: Technical environments must be able to be scanned for vulnerabilities and weaknesses so they can be identified and addressed.
“October is a good opportunity to review your preparedness, identify gaps and make sure responsibilities and ways of working are clear before an incident occurs,” says Pernilla Rönn.
Pernilla Rönn’s checklist: five things to do in October
- Check whether your organisation is covered by the rules and has registered. Since 1 July, registrations have been received by the National Cyber Security Centre (NCSC) at the Swedish National Defence Radio Establishment (FRA). Changes must be reported within 14 days.
- Review the new regulations on security measures against your existing procedures before 1 October, or as soon as possible.
- Schedule management training and document that it has been completed.
- Test your incident response process. Practise how a cyber incident would be managed and reported. Make sure everyone knows their responsibilities: an initial notification of a significant incident must be submitted within 24 hours, followed by an incident report within 72 hours and a final report within one month.
- If you manufacture connected products, prepare for CRA reporting. The reporting obligations have applied since 11 September. Make sure you have EU Login access and procedures for reporting through ENISA’s platform.
Contact
Region HiQ Group
Jenny Burman
Global PR and Communications Manager
Hi 👋 I’m Jenny, and I work with PR and communications at HiQ. Want to learn more about the great solutions we’re working on, or have questions about HiQ as a company? Don’t hesitate to get in touch!